Vulnerabilities — Page 20
Microsoft and Apple Rush Out Patches for Flaws That Let Attackers In Without a Password
Several of the Microsoft bugs score a perfect 10 out of 10 for severity. Apple quietly fixed a flaw that lets someone access your screen without logging in.
Google Patches 41 Security Flaws in Chrome 151, Six Rated Critical
The latest Chrome update fixes a cluster of memory-safety bugs that could let attackers crash your browser or run malicious code on your device. Here is what happened and what you should do.
The Security Metric That Lies: Why Knowing Your Vulnerabilities Is Not the Same as Reducing Your Risk
Security teams are drowning in vulnerability reports yet still can't answer the one question that matters: are we actually harder to attack today than we were last year? The old way of measuring risk is the problem.
Zapscape flaw in Linux KVM lets a rogue guest break out to the host
A newly disclosed bug in the Linux kernel's virtualization layer, tracked as CVE-2026-64561, could let an attacker inside a nested virtual machine reach the physical server underneath.
Cisco Patches a Dozen Flaws in SD-WAN and IOS XE, Three Rated Critical
An internal Cisco security review turned up 12 vulnerabilities, including three with a severity score of 9.8 out of 10, in software that runs corporate networks worldwide.
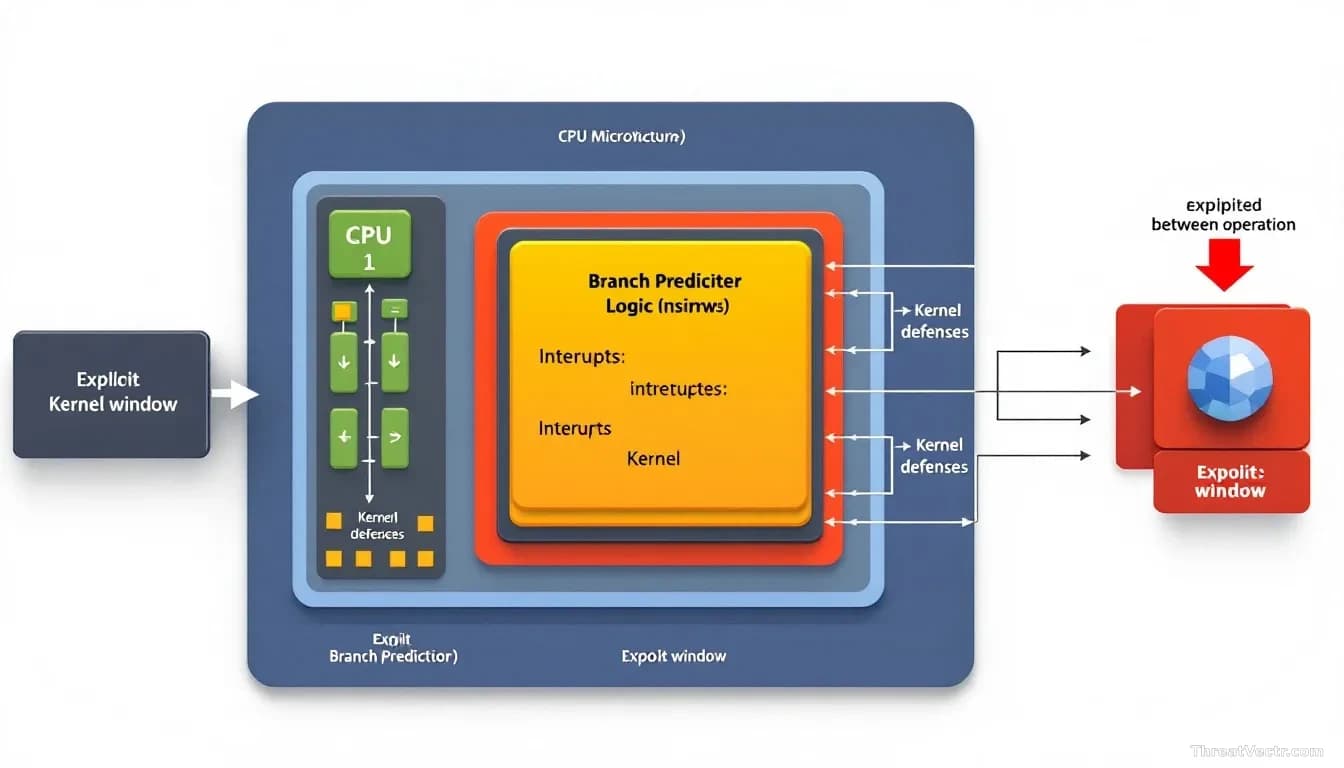
Researchers Sneak Past Spectre v2 by Slipping Between the Kernel's Own Defenses
MIT CSAIL's 'Interrupt Injection' technique re-poisons the branch predictor in the tiny window after the CPU cleans it and before Linux uses it.
ABB Ability Zenon ships with a MongoDB version that hasn't been patched since 2020
Industrial software used in energy and water plants bundles an old database carrying flaws that can leak memory and sidestep access controls.
The Window Between a New Vulnerability and an Active Attack Is Getting Shorter
Security teams are buried in alerts while attackers move faster than ever. The real problem isn't a shortage of warnings. It's knowing which ones actually matter before criminals act on them.
Most companies understand CTEM. Almost none of them can run it.
Knowing the five phases of Continuous Threat Exposure Management is the easy part. Building a system that actually proves your defences are improving is where programmes fall apart.
iCloud Private Relay Has a Leak: Researchers Show How Safari's Privacy Shield Can Spill Real IPs
A flaw in how Apple's WebKit handles certain web requests lets sites see the IP address Private Relay was meant to hide.
A 12-year-old flaw in a popular crypto library drained $5.7 million from wallets
Security firm Coinspect traced a wave of wallet thefts to a weak random number generator inside CryptoJS, a JavaScript library used by five cryptocurrency wallet apps to create recovery phrases.
Patched Doesn't Mean Safe: Why Security Teams Need to Test After They Fix
A new survey of 750 security leaders finds that fewer than one in three organisations check whether a fix actually stopped an attacker. The gap between completing work and reducing risk is where breaches still happen.
Cisco Patches 24 Flaws, Including a Perfect-Score Bug That Hands Attackers Full Control
A flaw in Cisco's firewall management software scores a rare 10 out of 10 on the severity scale, meaning a remote attacker needs no password to take complete control of an affected system.
Hackers Are Actively Exploiting a Critical Flaw in JetBrains TeamCity
A software tool used by thousands of development teams has a severe security hole that attackers are already using. The US government is giving federal agencies three days to fix it.
Why Modern Hackers Walk In Through the Front Door of Your Website
Security teams have spent years locking up their networks and servers. A new wave of attacks shows that criminals are now coming in through web applications instead, and most defences are not keeping up.