Vulnerabilities — Page 21
Fixing One Hole at a Time Is No Longer Enough: Why Security Must Follow the Full Attack Path
Criminals no longer stop at the front door. They chain weaknesses across apps, accounts, and cloud systems, and security teams testing each piece in isolation are missing the bigger picture.
Your Email's Design Layer Can Steal Your Password. No Suspicious Attachment Required.
Security researcher Gareth Heyes found that CSS, the code responsible for how emails look on screen, can be turned into a data-theft tool inside popular webmail services. No malicious files. No links to click.
15 Flaws in TP-Link Kit Put Automatic Network Setup at Risk
Security researchers found 15 vulnerabilities in TP-Link's Omada networking system and warn that the convenient zero-touch setup process millions of organisations rely on could hand criminals the keys to an entire network.
Researchers Cracked Samsung Phones Wide Open by Turning Bixby Against Its Own Device
A five-step exploit chain using Bixby, Samsung Members, and Samsung Account could hand a stranger complete control of your Galaxy phone. Patches are out, but older devices may still be exposed.
CISA gives federal agencies three days to patch Langflow, N-central and Tomcat flaws under active attack
Three separate bugs, three sets of criminals, one very short deadline. Here is what is being exploited and who should care.
Veeam Console Bug Hands Over Agent Credentials; Terraform MCP Server Leaks Tokens Between Users
Eleven fixes across HashiCorp, Veeam and Django include a 9.5-rated Veeam flaw and a cross-tenant Terraform MCP Server bug that hands one customer's cloud token to the next caller.
Linux Kernel Flaw 'OVSwrap' Hands Local Users Root on Around 800 Builds
A memory corruption bug in Open vSwitch, tracked as CVE-2026-64531, lets ordinary users on default Linux systems become administrator, and a working exploit is already public.
CISA Adds Three Actively Exploited Bugs to Its Must-Patch List
A critical Langflow flaw joins Apache Tomcat and N-central issues on the U.S. government's Known Exploited Vulnerabilities catalog after evidence of live attacks.
Credential-Stealing Worm Spreads Across npm Packages
A worm seeded in a single npm package replicated into hundreds of others on August 4, 2026, with two security firms putting the damage count at different but alarming numbers.
AI Meeting Bot Tl;dv Left Government and Corporate Calls Wide Open
A security researcher found a misconfigured database in the popular meeting-recording app tl;dv that let anyone see live government and corporate video calls, and, in most cases, join them uninvited.
Fifteen Flaws in TP-Link's Auto-Setup System Could Hand Hackers Control of an Entire Business Network
Forescout found serious weaknesses in the technology TP-Link uses to automatically configure routers, switches, and cameras. Chain enough of them together and an outsider can quietly seize every device on the network.
cPanel patches critical database flaw that let hosting customers run SQL as root
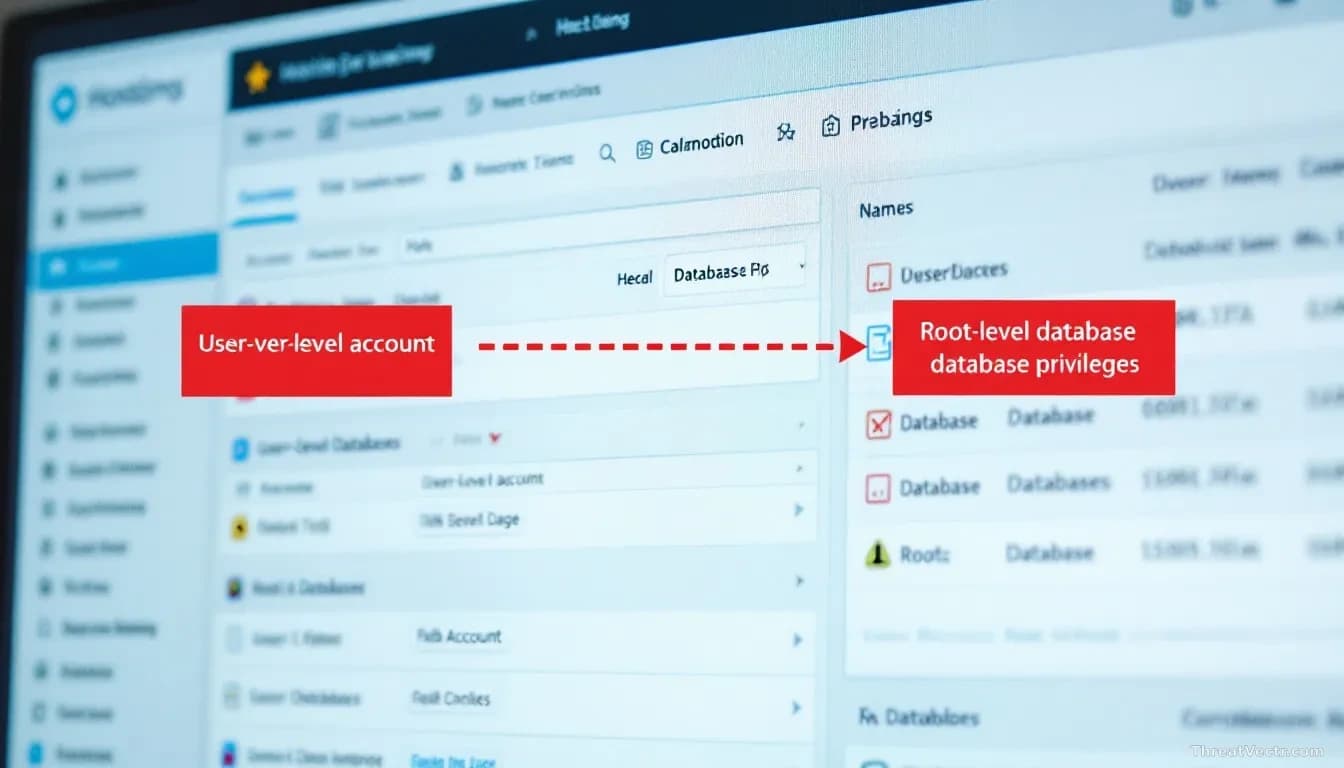
A newly disclosed bug, CVE-2026-58048, crossed the line between a single hosting account and the server's master database identity. cPanel has shipped a targeted fix.
Microsoft Paid Out $20 Million in Bug Bounty Rewards This Year
More than 560 security researchers from 64 countries were paid to find and report software flaws. Not everyone is happy about how the company handled the work.
CISA flags N-able N-central bug as actively exploited, orders federal fix
The remote monitoring platform used by thousands of IT providers carries an authentication bypass that attackers are already using in the wild.
Thermo Fisher patches DNA analysis flaw that could let evidence files be quietly altered
A vulnerability in Applied Biosystems human identification software could allow near-invisible edits to forensic DNA files before analysts ever see them.