Opinion — Page 3
Your Vendors Are a Risk You Cannot Ignore. Here Is How Boards Should Own It.
Most companies review their suppliers and tick the boxes. Far fewer can say how much financial damage a vendor failure would actually cost them. That gap is the problem.
Your dashboards are not your defence: why 'visibility' is not the same as surviving an attack
Security teams can monitor everything and still lose everything. A quietly influential argument making the rounds says the industry has confused watching a system with being able to keep it running, and the gap is getting harder to ignore.
The Summer Everyone Launched a Clearinghouse
Vendor announcements have piled up fast. But not every 'clearinghouse' is a fresh idea, and the differences matter more than the marketing suggests.
From Unusual Path to the Top: What Tarah Wheeler's Career Tells Us About Who Gets to Lead in Cybersecurity
Tarah Wheeler is CISO at TPO Group, a firm advising organisations where security failures carry real-world consequences. Her route there looked nothing like the standard playbook.
Buying an AI SOC in 2026? Here's How to Tell the Real Thing From a Chatbot in a Trench Coat
Vendors are shouting the same three letters. The products behind them are wildly different, and the wrong pick will cost you a year.
The Cybersecurity Skills Gap Is Real. But We're Measuring the Wrong Thing.
Companies keep buying courses and certifications. Breaches keep happening anyway. The problem is not a shortage of trained people. It is a shortage of people who have actually practised under fire.
Seven Cyber Risk Assessment Mistakes That Give Security Leaders False Confidence
Organisations tick boxes, skip awkward corners of their networks, and confuse passing an audit with being secure. Here is what actually goes wrong.
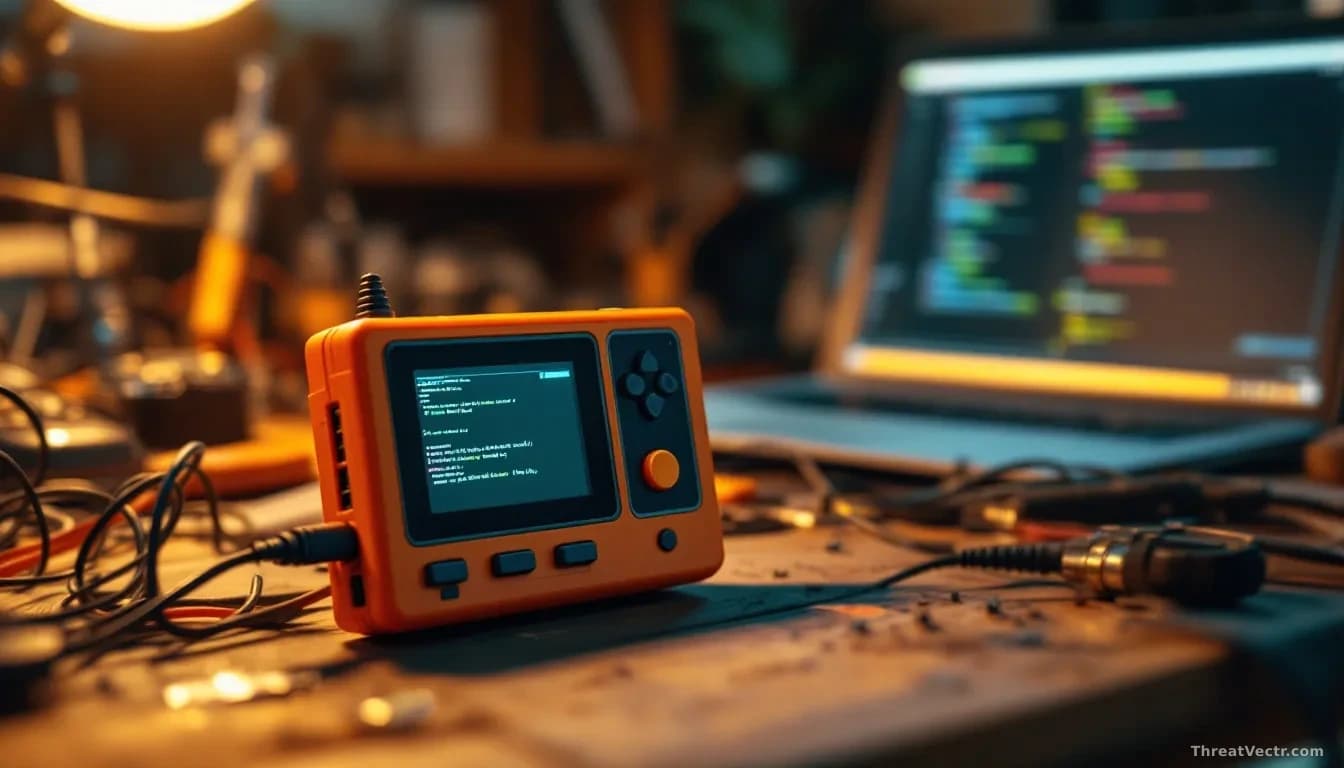
Flipper Zero firmware goes into maintenance mode as company hands the wheel to volunteers
The pocket-sized hacking gadget's maker is shrinking its firmware team and letting the community vote on what gets built next.
The 2026 Vendor Survey Nobody Asked For, Except The Findings Actually Track
The Bitdefender Cybersecurity Assessment polled 1,200 practitioners and concluded awareness is up and resilience is flat. Anyone running production already knew that.
Why SOCs Still Can't Answer 'What Happened?' — The Case for Network Detection
Alert-driven triage keeps missing context. NDR proponents argue packet truth is the only ground truth left.

RSnake's Case for a CISO Code of Ethics
Robert Hansen argues that kickbacks, no-show jobs, and shelfware deals aren't just embarrassing, they're a national security problem.
The Patch Cycle Won't Survive Machine-Speed Adversaries
Defenders measured dwell time in days. Agentic attack pipelines are about to measure it in minutes.
One Executive, Two Hats: Carl Froggett on Running Security and IT at Deep Instinct
The former Citi CISO talks about what happens when security leadership and infrastructure ownership collapse into a single role.
When the Trigger Pulls Itself: Agentic AI and the End of the Human-in-the-Loop
Every weapon in history extended a human decision. Agentic systems are the first that try to replace it, and the security implications are not theoretical.
From Prevention to Resilience: Cybersecurity’s New Paradigm
Breaches are no longer a matter of if. The question is whether your organisation can keep functioning when one lands.