#ransomware
155 stories taggedransomware · page 6 of 11.
Fake IT support calls on Microsoft Teams are ending in ransomware within a day
A gang tracked as STAC4749 is phoning staff on Teams, pretending to be helpdesk, and locking company files with Chaos ransomware in under 17 hours.
Ransomware Group Spacebears Claims Attack on StellarRAD Systems
A criminal group has listed the US telecoms-software firm on its dark-web pressure site, alleging stolen employee data and financial records. The company has not confirmed any incident.
The Four Ways Criminals Beat Multi-Factor Authentication (And What You Can Do About It)
Multi-factor authentication was supposed to be the lock that hackers couldn't pick. It turns out there are at least four reliable routes through it, and most organisations are leaving at least one wide open.
Ransomware gangs are going after VPNs, and an AI just ran its own attack
Ransomware attacks rose for the fourth month in a row in June, with criminals targeting the devices companies use to connect remote workers. A new AI-driven attack completed an entire break-in with no human at the keyboard.
PEAR ransomware crew claims 1.26 million-record breach at Georgia billing firm MCBS
Medical Computer Business Services says attackers roamed its network for four days in September 2025. A ransomware group now claims it stole 3.3 terabytes of patient and business data.
How the FBI Took Down LockBit by Destroying the One Thing Criminals Can't Easily Replace: Trust
Operation Cronos didn't just seize servers. It turned LockBit's own website against its partners, shattered the group's reputation, and cut US ransom payments by 79 percent in the second half of 2024.
Your ransomware playbook is probably putting the wrong person in charge at 4 a.m.
A growing body of evidence shows that the real damage in ransomware incidents often comes not from the attack itself, but from who gets to decide whether to pull the plug on a business-critical system.
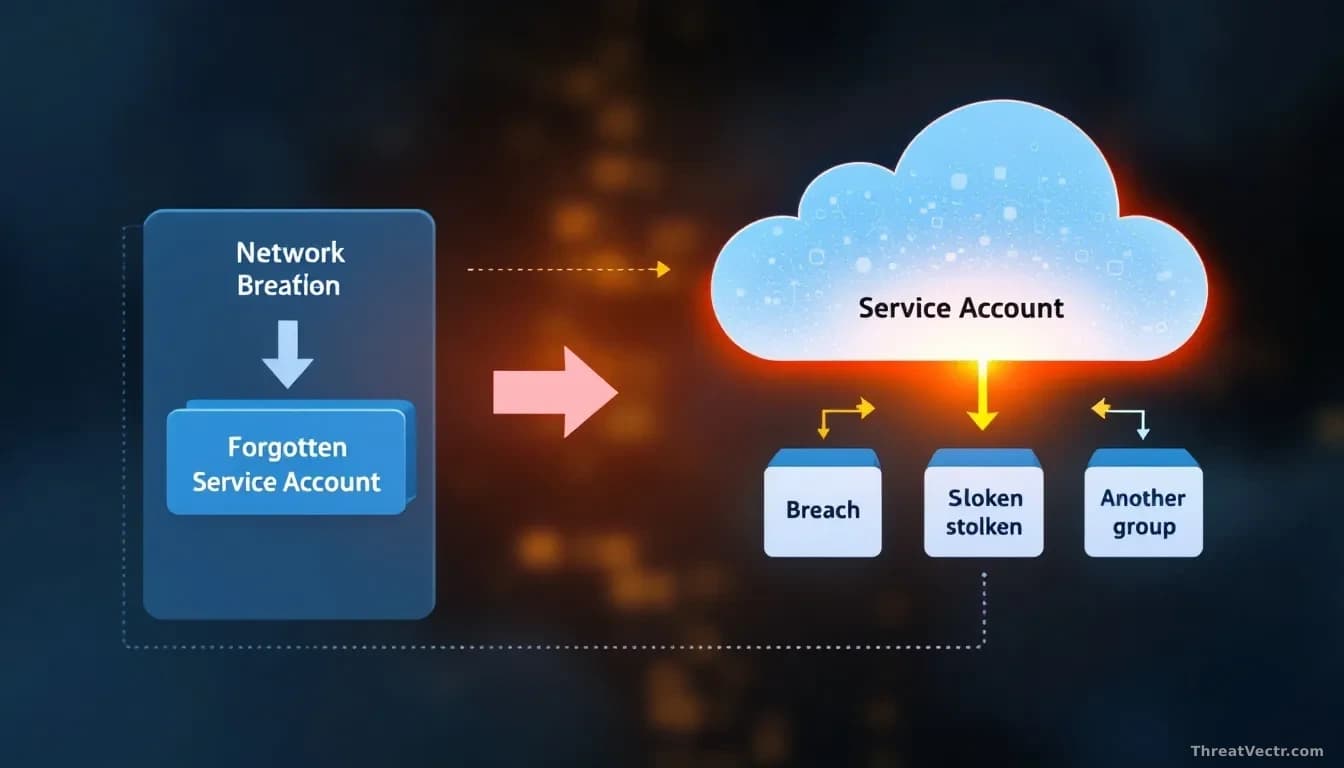
The Hackers Got Hacked: Inside the Klue Breach and What It Means for Every Business Using Cloud Software
A forgotten service account let criminals walk into a competitive-intelligence platform. Then a second criminal group stole the stolen data. The whole chain shows exactly how cloud software trust goes wrong.
DevMan Ransomware Runs a One-Stop Web Portal for Its Criminal Affiliates
Swiss researchers say the operation, tracked as Funky Mantis, gives partners a single dashboard to build malware, chase payments, and manage victims.
OnTrac tells customers hackers were inside its network for three days in March
The last-mile delivery firm hints at a quiet deal with its attackers, but no ransomware crew has claimed the hit.
Three Security Stories You May Have Missed: Industrial Switches, Russian Email Spying, and a Rail Ransomware Shakedown
Flaws in Siemens industrial network hardware, a Russian espionage campaign targeting Zimbra webmail servers, and a ransomware extortion attempt against Swiss train maker Stadler Rail.
Europol Pulls 4,340 Links Tied to 'The Com' Extortion Network
A nine-country push targets an online ecosystem that grooms minors, spreads violence manuals, and has been linked to ransomware attacks on Marks & Spencer and Las Vegas casinos.
CISA orders three-day fix as Clop hits PTC Windchill flaw
A critical bug in PTC's product design software, CVE-2026-12569, is being used by the Clop extortion crew to steal corporate data. Regulators in the US and Germany moved fast.
Hackers Are Actively Exploiting a Flaw in Check Point Security Software
A newly discovered hole in Check Point's network management tools let attackers log in as administrators without a password. Real attacks were already happening before the patch arrived.
What is ransomware-as-a-service? A plain-English guide
Ransomware-as-a-service lets criminals rent attack tools from developers, the same way businesses subscribe to software, making large-scale extortion attacks available to almost anyone.