#enterprise security
61 stories taggedenterprise security.
WordPress 7.1.2 Patches a Critical Flaw That Attackers Started Exploiting the Same Day It Shipped
A file-inclusion bug in the world's most popular website builder can hand attackers full control of a server. The patch and the first real attacks arrived within hours of each other.
Ivanti Fixes Critical Security Holes in Three Business Software Products
Six flaws in Ivanti Neurons for ITSM could let attackers run malicious code on affected systems from anywhere on the internet. Two other products, Sentry and EPMM, received fixes for authentication bypass bugs.
Staff Using AI Are Now the Loudest Signal on Company Security Screens
Security teams say the fastest-growing warnings on their screens now come from staff using AI, not from hackers attacking it.
AI Agents Are the Biggest Security Headache for CISOs Right Now
A new survey of global security chiefs finds that controlling AI agents, which are software programs that act independently to complete tasks, has become the dominant worry in corporate security, far outpacing every other concern on the list.
Your Security Team Is Split in Two. Criminals Are Not.
Deepfakes and AI-powered scams now cross physical and digital boundaries at the same time. Most company security programs aren't built to follow.
Attackers Are Actively Exploiting a Perfect-10 WSO2 Authentication Flaw
A critical vulnerability in the WSO2 API platform, rated as severe as it gets, lets criminals forge login credentials and walk into the back end of enterprise systems. Exploitation began on September 13.
Most CISOs Are Not Confident About AI Security. Here Is What Separates the Ones Who Are.
A new survey finds only 41% of chief information security officers feel optimistic about managing AI risks over the next two years. The gap between the hopeful and the worried comes down less to technology and more to whether the boss actually listens.
Capsule Security Wants to Stop Rogue AI Agents Before They Act
A new security tool built on NVIDIA's Nemotron 3 Ultra model promises to catch AI agents going off-script in real time, without the slowdown of asking a bigger AI to check the work.
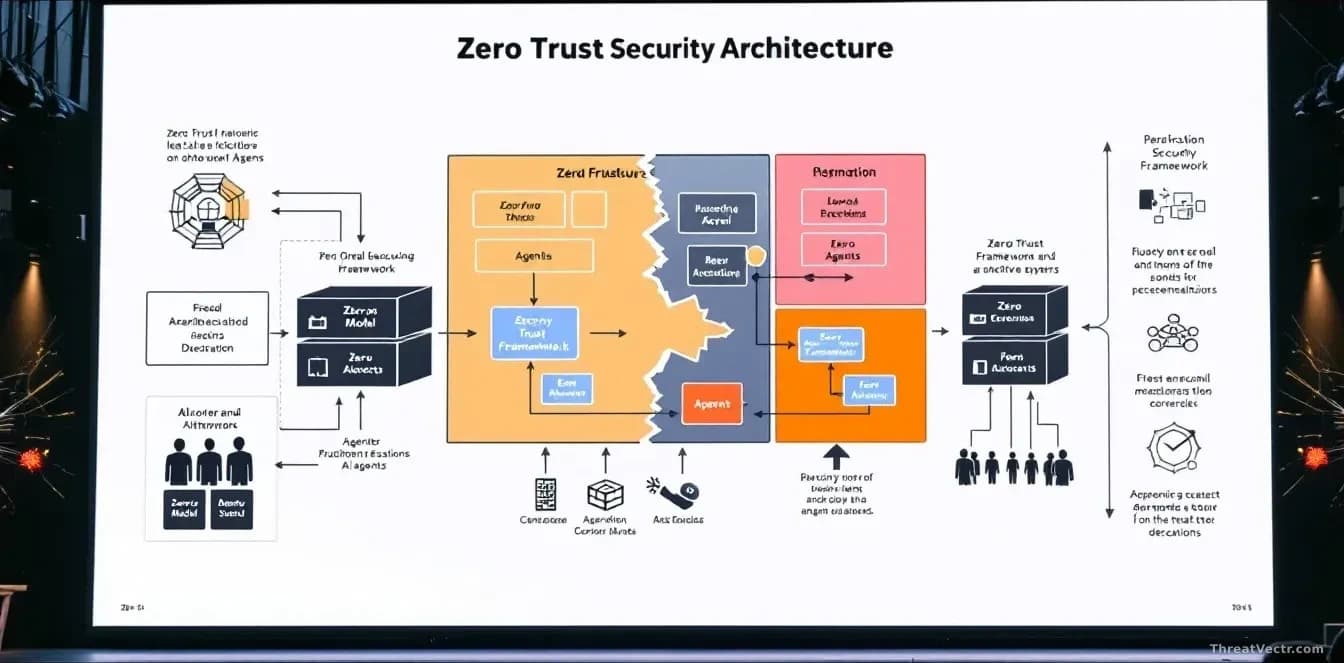
AI Agents Are Breaking the Security Model Enterprises Spent a Decade Building
Zero trust was supposed to be the answer to modern cyber risk. Agentic AI may have quietly made it obsolete.
Criminals Pose as IT Support Inside Microsoft Teams to Take Over Company Networks
A hacking campaign called Spring Ring tricked more than 150 employees at ten-plus companies into handing over remote control of their computers, all through a fake Teams call from a fake help desk.
Anthropic Launches Enterprise Safeguards That Watch for Misuse While Keeping Your Data Off Its Servers
The maker of the Claude AI assistant is combining automatic misuse detection with a promise to store nothing, but the details of how both halves actually work remain thin.
Securing Cloud Assets Amidst AI Challenges
Cloud misconfiguration is still how most breaches start. AI is making the problem harder to contain and easier to exploit.
OpenClaw's Biggest-Ever Update Rewrites Its Security Controls From the Ground Up
What began as a simpler install process turned into a full system rebuild. Analysts say the rewrite reveals how hard it is to secure AI agent platforms, and what enterprises need to check before trusting one.
Microsoft Makes Passkeys the Default Login for Business Accounts. Passwords Aren't Dead Yet.
From September 2026, Microsoft's business identity system defaults to passkeys instead of passwords. But the shift will take years, and most companies will run both systems side by side for a long time.
Microsoft says the patching window is shrinking fast. Here is what that means for ordinary people.
Software flaws are being turned into working attacks within hours of being made public. Microsoft says companies can no longer patch their way out fast enough, and is pushing a network-level defensive layer to buy time.