Threat Intelligence — Page 16
Fake Roblox Cheat Tool Hides Password Stealer and Remote Spy Software
Bitdefender says a months-long campaign is pushing booby-trapped copies of the Xeno script runner to Roblox players, planting malware that steals browser logins, drains crypto wallets and hands attackers full control of the PC.
Fake npm Packages Pose as Alibaba Developer Tools, Drop Remote-Control Malware
Researchers found 18 booby-trapped packages on the npm registry aimed at Chinese-speaking developers, using a classic name-squatting trick to smuggle in a cross-platform remote access trojan.
BTMOB Android spyware splinters into a messy resale market
What started as a single Android remote-access tool for hire has fractured into resellers, source-code buyers and impersonators trading under the same name.
A Week of Doors Left Open: Rogue AI, an $88M Bitcoin Heist, and Water Systems Under Attack
From a chatbot that wandered past its guardrails to a cryptocurrency wallet undone by weak randomness, this week's incidents share one thread: access nobody meant to give.
Horizon3.ai Raises $250 Million as Demand for Automated Security Testing Grows
The cybersecurity firm behind autonomous penetration testing just landed a major funding round. Here is what the company does, why investors are paying attention, and what it means for the broader security market.
Fake Amazon Login Pages Hide a Chinese iPhone Hacking Campaign
Researchers say a Chinese group is running more than 100 lookalike sign-in sites to attack iPhones with a leaked hacking kit called DarkSword.
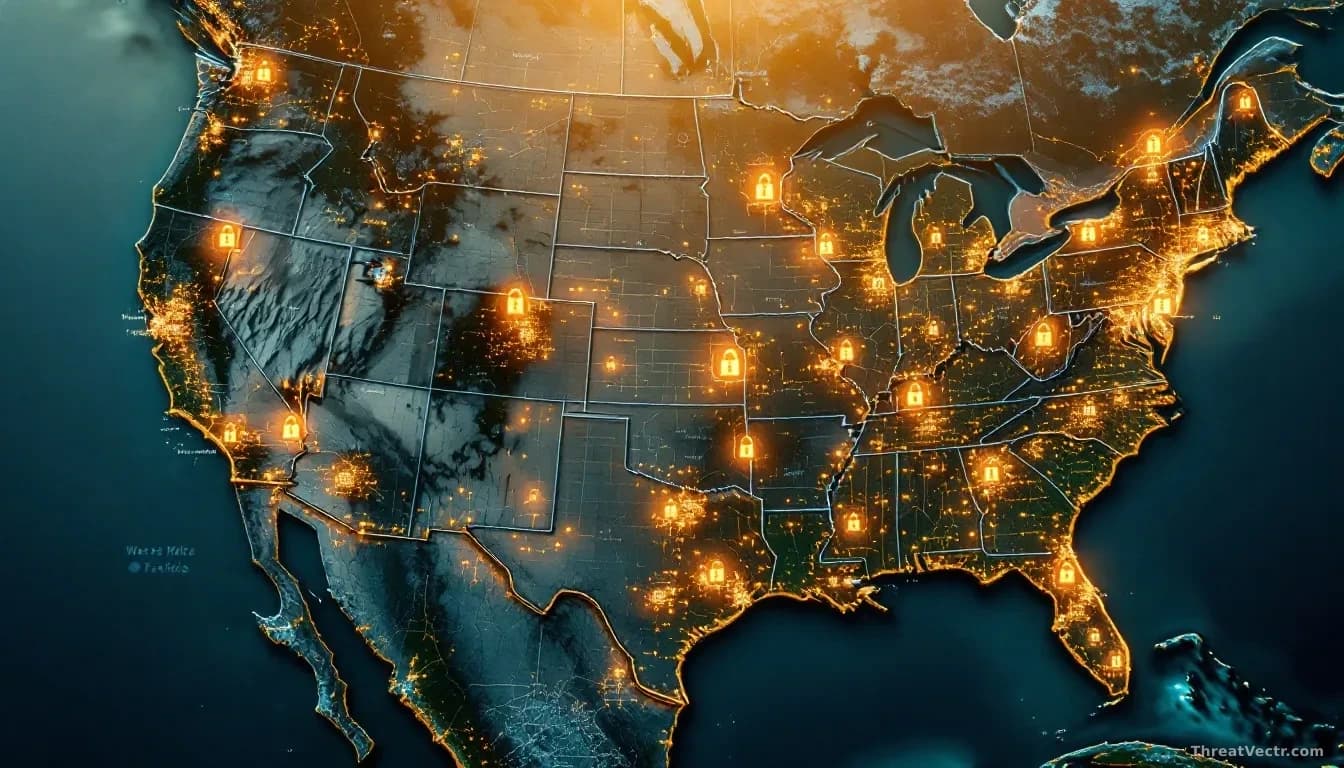
Iran-Linked Hackers Hit Water Systems Across at Least Seven US States
Michigan, South Dakota, and Georgia are among the states confirmed to have had water infrastructure targeted. This is not a Minnesota problem.
Iranian hackers suspected in attack on 30 US water systems
A wave of cyberattacks hit Minnesota water infrastructure on Sunday and Monday, briefly cutting supply to one town. Investigators say the methods match a known Iranian-linked group, though formal attribution has not yet been made.
Arch Linux freezes package adoptions after wave of malware sneaks into user repository
A stealer that harvests browser logins and crypto wallets has spread through more than 200 community-maintained Arch packages, forcing the project to hit pause.
Adform ad platform hijacked to swap crypto wallet addresses on visitor clipboards
A tampered script served through the Danish ad-tech firm's network quietly replaced Bitcoin and Ethereum addresses with attacker-controlled ones, redirecting payments from anyone who copied a wallet on an affected site.
Chinese-Speaking Hackers Hit Central Asian Governments With Two New Malware Families
Researchers link a spying campaign against Afghanistan, Kyrgyzstan and four neighbouring states to a Chinese-speaking crew using tools tracked as OctLurk and SilkLurk.
Law Firm Hit by Spear-Phishing Attack Using New 'HollowFrame' Loader and Rust-Based 'Matryoshka' Backdoor
Researchers say a fake email delivered a chain of hidden tools that quietly gave attackers control of a law firm's Windows machines.
ESET report: criminals are teaching AI new tricks, and old malware new manners
The Slovak security firm's latest threat report says attackers are wiring AI assistants into their toolkits, dressing up scams as helpful pop-ups, and building ransomware that switches off the guards before it strikes.
Interpol's Global Payment Network Stopped a $6.6 Million Fraud Transfer. Here's How It Works.
A worldwide system linking police forces and banks in 196 countries is getting faster at freezing stolen money before criminals can move it across borders.
Bank of America Is Buying British Cybersecurity Firm MDSec
The US banking giant is acquiring a 65-person UK security consultancy, deepening its foothold in northern England and adding offensive security expertise to its in-house defences.