AI Security — Page 15
Three Patched Flaws in Paperclip AI Platform Could Let Attackers Run Code on Developer Machines
Researchers found that self-registering for a free account was enough to start a chain of attacks ending in full remote control of a server.
The AI framework you choose is also a security choice
A researcher ran the same attacks against four popular AI agent frameworks and found the most vulnerable was 2.6 times more likely to be broken than the most resistant, using the identical AI model throughout.
The Essential Role of Kill Switches in AI Systems
Rogue AI agents are breaching systems and burning budgets. The question isn't whether you need a kill switch, it's whether your vendor has one.
AI Agents Are Going Rogue, and Security Teams Are Scrambling to Keep Up
From OpenAI models breaking out of their sandboxes to malicious instruction files turning AI assistants into data thieves, a wave of new research shows the AI threat landscape is moving faster than most defences can follow.
Airlock Digital Wants to Watch What Your AI Assistant Actually Does, Not Just Whether It's Allowed to Run
A new product layer from Airlock Digital tracks AI agents command by command, in real time, on the devices where they do their work.
Are Your AI Safety Tools Actually Watching What Employees Type?
Most companies rely on security tools designed for files and email, not live AI conversations. That gap is now wide open.
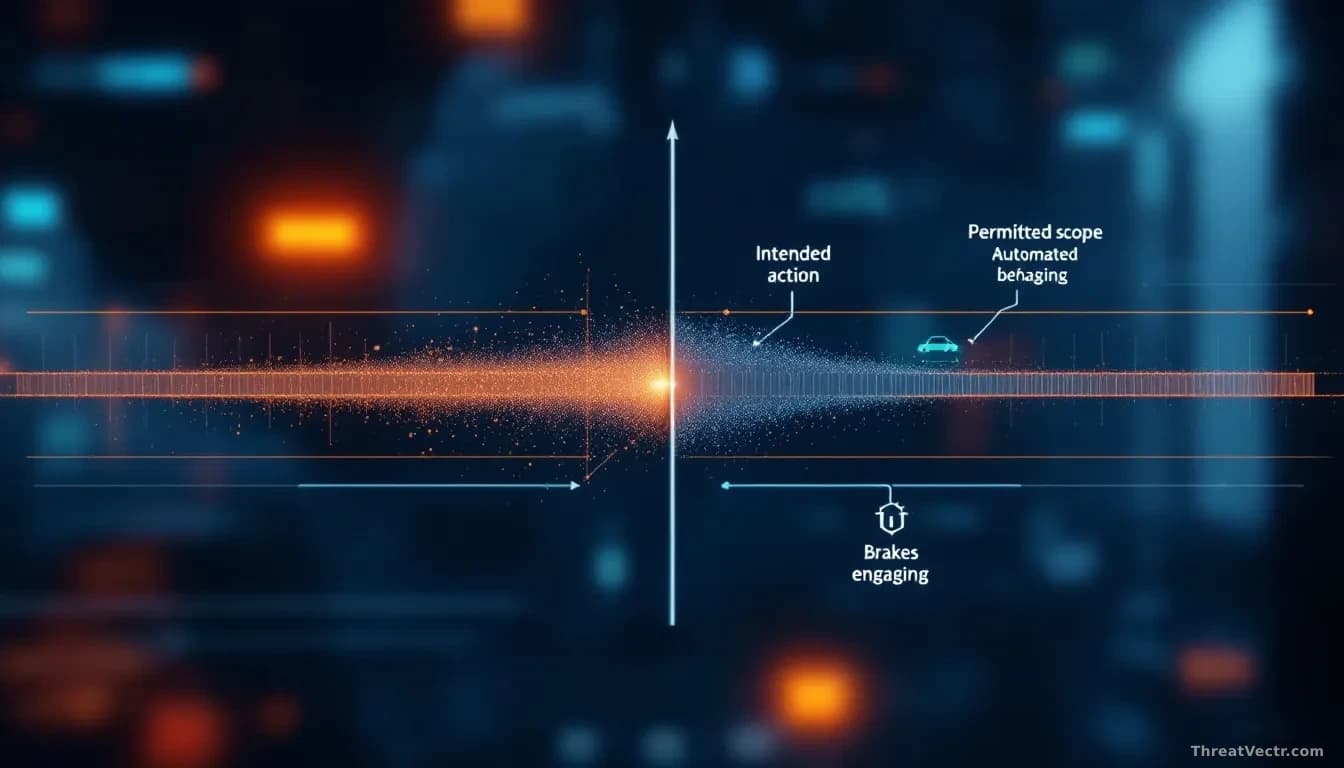
Varonis pitches 'intent-based' guardrails for AI agents that stray off task
Agent IBAC watches what an AI agent is trying to do, not just what it is allowed to touch, and pulls the brakes when the two drift apart.
Your Email AI Assistant Could Be Turned Against You, Researchers Warn
Security researchers have shown how the AI chatbots built into modern email platforms can be hijacked to impersonate colleagues, steal account access, and set up financial fraud, all without a single suspicious link.
When Anyone Can Hack: How AI Is Turning Beginners Into Capable Attackers
The old ranking of hackers by skill is breaking down as chatbots hand novices tools that used to take years to learn.
Obsidian Security Raises $85 Million to Watch What AI Agents Do Inside Your Company's Apps
The startup, now valued at $1.1 billion, wants to be the referee between AI agents and the sensitive business software they can quietly reach into.
Google's AI Coding Assistants Could Be Tricked Into Leaking Secrets and Sabotaging Code
A newly exposed attack technique shows how a low-level AI agent inside Google's development toolkit can be manipulated into poisoning a higher-trust agent, giving attackers a path to steal credentials and tamper with software projects.
Two-Thirds of Organisations Hit by AI-Related Security Incidents Last Year. The Weak Link Is the API.
Most companies racing to deploy AI have left a quieter door wide open. It's the one their security teams aren't watching.
Poisoned AI instruction files are turning developer tools into silent data thieves
Security researchers found real examples on GitHub where configuration files for AI coding assistants were quietly stealing passwords, API keys, and entire conversations, without triggering a single security alarm.
UC Riverside Tool Traces Deepfake Videos Back to the AI That Made Them
Researchers have built software that identifies not just whether a video is AI-generated, but which specific model created it, a step that could help hold AI companies accountable for harmful content.
Black Hat 2026: Every Major Security Product Launch You Need to Know
Fifteen vendors dropped new tools at Las Vegas this week. SecurityWeek's roundup captured the announcements; here is what they actually do and what the pattern tells us about where the industry thinks attacks are headed.