#third-party risk
19 stories taggedthird-party risk.
FBI and CISA warn critical infrastructure operators to rein in third-party ICS integrators
A new joint fact sheet asks water, power and manufacturing operators to lock down the outside engineers who quietly run their control systems.
The Google Workspace apps you forgot about are still reading your email
Third-party integrations left connected to Workspace tenants keep their access for years, and attackers are quietly walking through the door they left open.
Veradigm Confirms Patient Data Theft After Vendor Credentials Stolen; Ransomware Crew Claims 3.5 Million Records
The Chicago health-tech firm told the SEC that attackers used a vendor's login to a customer-service API. The Gentlemen ransomware group says it grabbed millions of patient records.
Most CISOs Are Not Confident About AI Security. Here Is What Separates the Ones Who Are.
A new survey finds only 41% of chief information security officers feel optimistic about managing AI risks over the next two years. The gap between the hopeful and the worried comes down less to technology and more to whether the boss actually listens.
McKesson Confirms Break-In After Hackers Claim 284 Million Patient Records Stolen
The US pharmaceutical distribution giant says intruders reached third-party apps holding limited data. The ShinyHunters gang claims a haul far larger than McKesson admits.
Quest Apartment Hotels Investigating Customer Data Breach Tied to Third-Party Provider
Personal details of Quest guests, including names, email addresses and some dates of birth, were exposed after criminals broke into a database through a flaw in an outside supplier's system.
SickKids Says Third-Party Software Flaw Exposed Employee and Applicant Data
Toronto's largest paediatric hospital confirms a breach affecting HR records. Patient files were not touched.
A Survey Company May Have Leaked Scottish Government Workers' Personal Details
A contractor hired to run a government training exercise lost staff data from Scotland's public prosecution service. The real worry: dozens of other agencies probably handed over the same information.
LexisNexis Pulls Three Services Offline After Vendor Server Break-In
The data analytics giant disconnected Nexis Diligence, Metabase API and Newsdesk after spotting suspicious activity on a third party's servers, and is rebuilding the systems from scratch.
Compliance Alone Won't Protect Your Organisation: Edna Conway on the Real Future of Cyber Risk
A cybersecurity veteran with four decades in the field says ticking regulatory boxes is not the same as being secure. Here is what she means and why it matters.
Your Company's Vendor Problem Starts Before Anyone Calls Security
When businesses pick software first and ask security questions second, they hand criminals a head start. Here is why fixing that order matters, and what a grown-up process actually looks like.
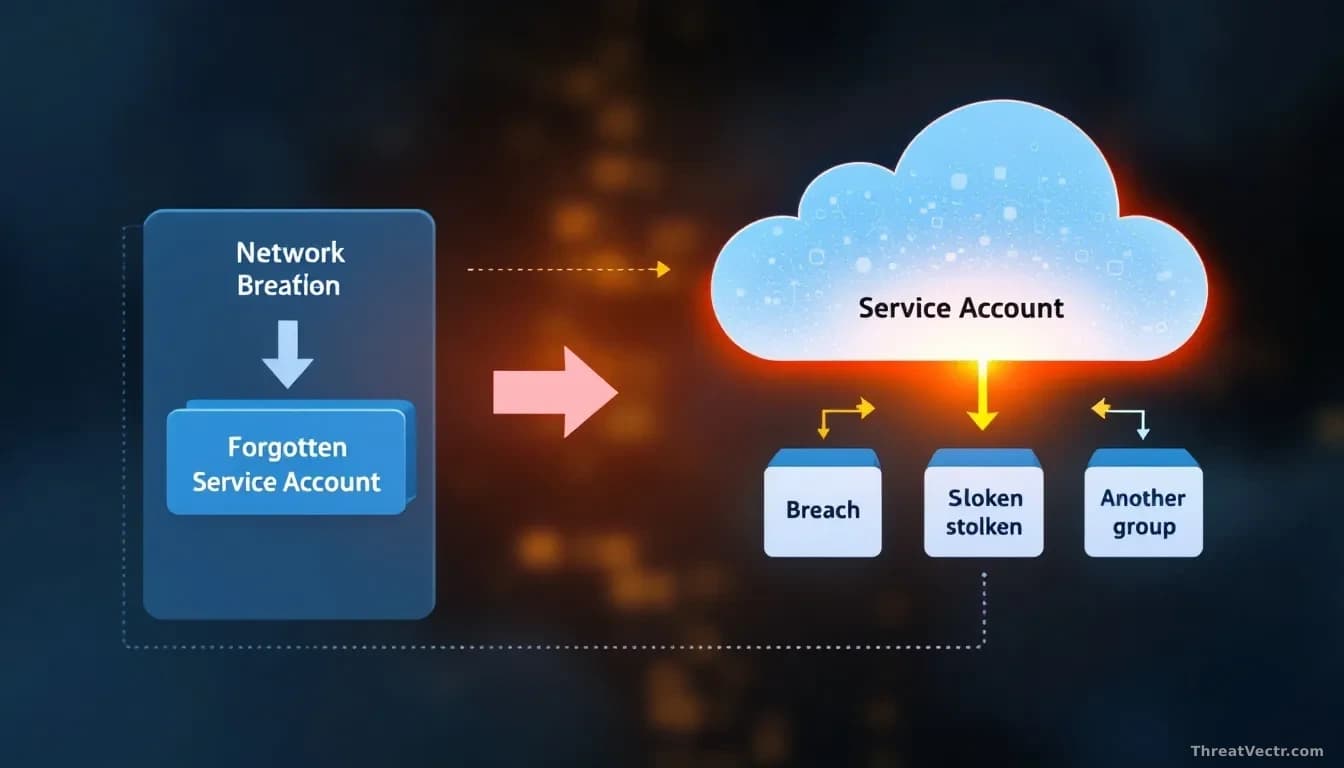
The Hackers Got Hacked: Inside the Klue Breach and What It Means for Every Business Using Cloud Software
A forgotten service account let criminals walk into a competitive-intelligence platform. Then a second criminal group stole the stolen data. The whole chain shows exactly how cloud software trust goes wrong.
Your Bank May Be Sending Your Loan Details to TikTok Without Knowing It
New research finds that tracking tools baked into banking websites are quietly forwarding customers' personal and financial data to advertising platforms, sometimes before anyone clicks 'accept cookies'.
Ernst & Young Client Data Stolen in Third-Party Platform Breach
Names, Social Security numbers, and card details belonging to Ernst & Young clients were taken after criminals broke into a third-party software platform the firm used to manage data.
Ernst & Young Tells Clients Their Tax Data Was Taken From a Support Ticket System
The Big Four firm says an outside party pulled documents from a third-party helpdesk platform between late March and mid-April. Affected clients get 24 months of identity monitoring through Experian.