#ShinyHunters
27 stories taggedShinyHunters · page 2 of 2.
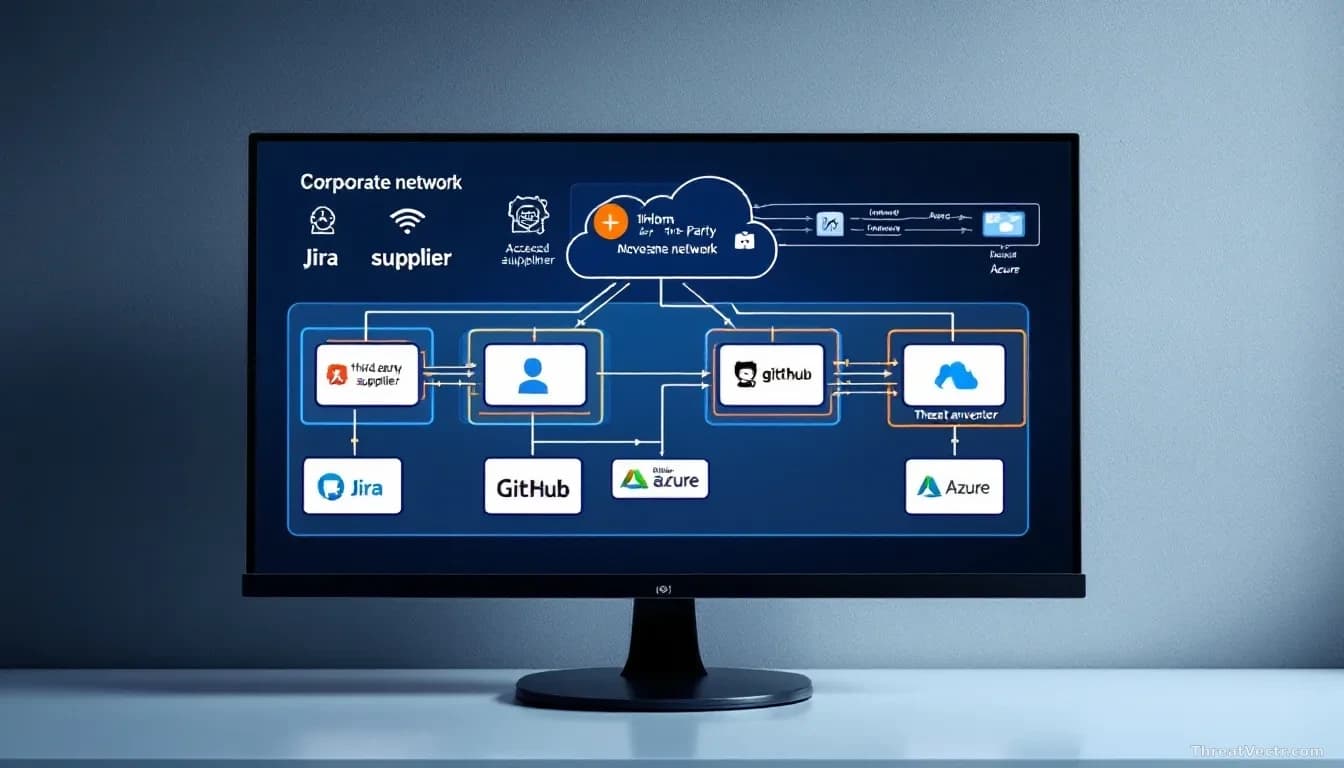
ShinyHunters claims Ernst & Young breach, points to supply-chain attack
The extortion crew says stolen credentials from a third-party supplier gave them access to EY's Jira, GitHub and Azure. The accounting giant has not confirmed the group's role.
DentaQuest Data Breach: Up to 23 Million People's Dental and Health Records Exposed
A three-day network intrusion at one of America's largest dental benefits administrators may have handed criminals the Social Security numbers, treatment records, and government IDs of tens of millions of people.
Scammers Recycle ShinyHunters Breach Data to Power $2,000 Sextortion Emails
A campaign running since April uses email addresses from old ShinyHunters leaks to make fake extortion threats look personal.
How ShinyHunters walked into Salesforce accounts without breaking anything
Microsoft says a year of data theft from Salesforce tenants leaned on trusted app connections, not a platform bug.
Dutch Police Say Local Hackers Helped Pull Off the Odido Breach That Exposed 6.2 Million Customers
A phone call to customer service, a fake IT worker, and a phishing page: how criminals allegedly walked out with data on nearly every Odido subscriber.
Helix: the new extortion crew phoning staff to raid SharePoint files
Researchers at ReliaQuest say the group impersonates managers on the phone, tricks staff into a login trap, then pulls company documents from Microsoft SharePoint.
ShinyHunters Breach Hits Medtronic: 3.8 Million Patients' Medical Records Stolen
The extortion group ShinyHunters broke into the medical device maker's systems in April 2026, walking away with names, Social Security numbers, and sensitive health details belonging to nearly four million people.
Medtronic tells customers their personal data was stolen in ShinyHunters raid
The medical device giant confirms hackers rifled through its corporate systems for nearly a week in April, exposing names, Social Security numbers and health details.
NAIC Says ShinyHunters Walked Out With Public Data and Stale Logs After PeopleSoft Zero-Day Hit
The regulator-of-regulators confirms an Oracle PeopleSoft zero-day was the entry point, but disputes the extortion crew's claims about what was taken.
ShinyHunters Doesn't Need Malware. That's the Point.
The group's latest breaches are a reminder that stolen credentials and patience beat zero-days most days of the week.
Oracle Patches PeopleSoft Flaw Tied to ShinyHunters Activity, Stays Quiet on Zero-Day Status
CVE-2026-35273 has a fix. Whether attackers got there first is a question Oracle isn't answering.
The Login Page That Demanded a Ransom
ShinyHunters defaced Canvas mid-finals week, taking the learning platform offline and exposing what one researcher calls an eight-month attack arc against Instructure.