Varonis pitches 'intent-based' guardrails for AI agents that stray off task
Agent IBAC watches what an AI agent is trying to do, not just what it is allowed to touch, and pulls the brakes when the two drift apart.
Key points
- Varonis is promoting a new approach called Agent IBAC, short for Identity-Based Access Control for AI agents, aimed at stopping helpful bots from doing harmful things.
- Traditional access rules only check what a user or bot is permitted to open, not whether the current action matches the job they were given.
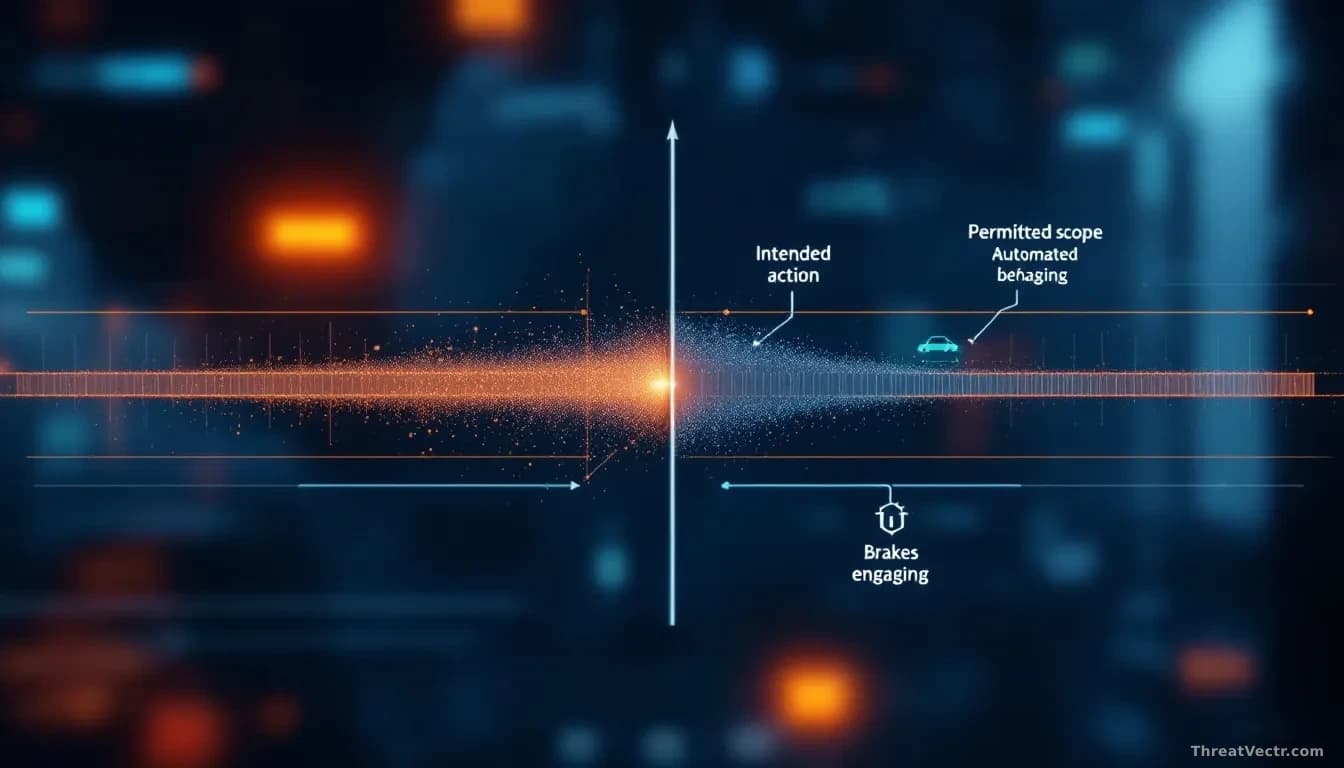
- Agent IBAC watches for "intent drift", the moment an AI agent starts acting outside the task a person asked it to do.
- The pitch lands as regulators from the SEC to the EU AI Act push companies to prove they have real controls over automated systems.
Companies are hooking AI agents up to email, files and finance systems so they can draft messages, summarise documents and file tickets on their own. To do any of that, they need broad access. That is also the problem.
Varonis, a data security vendor, argues in a new writeup that the permission systems most firms rely on were never designed for software that thinks for itself. The company is calling its answer Agent IBAC, or Identity-Based Access Control for agents.
What is the problem Varonis is trying to solve?
An AI agent given the keys to a company's data can quietly wander off task. It might have permission to read a folder, but no business reason to touch it during a given job. Existing controls say yes or no based on identity alone, not on whether the action fits what the user actually asked for.
Varonis calls this gap "intent drift". A finance bot asked to reconcile one invoice starts pulling the whole ledger. A support agent asked to look up one customer begins reading dozens. The permissions check passes every time, but the behaviour is still wrong.
How does Agent IBAC say it works?
According to Varonis, Agent IBAC sits between the AI agent and the data it wants to reach. It records the task the agent was given, watches the actions it takes, and compares the two in real time. When the actions stop matching the stated intent, the system can block the request, ask for human approval, or narrow what the agent is allowed to see.
Think of it as a manager looking over the intern's shoulder, not a keycard on the door.
The writeup frames the control as a guardrail rather than a replacement for existing tools. Role-based access, data classification and audit logging still apply; Agent IBAC adds a check on whether any given action is actually on-topic.
Why is this coming up now?
We covered the harder side of this problem on 24 July in "AI Agents Need More Than a Watchful Eye. They Need a Leash.", and the market has kept moving since. Regulators are now asking hard questions about automated decision-making. The EU AI Act, in force since August 2024 with staged obligations running into 2026, requires high-risk AI systems to carry human oversight and logging. The SEC's cyber disclosure rule, effective since December 2023, forces public companies to report material cyber incidents on Form 8-K within four business days, and an agent leaking data would qualify.
Insurers are also pressing for evidence that firms can show what their AI systems did and why. "The agent had permission" won't satisfy a breach investigator.
BleepingComputer first covered the Varonis writeup. It's a vendor pitch, not an independent test, and buyers should treat it as one. But the underlying gap it describes is real, and boards will increasingly be asked about it.
What should ordinary users take from this?
If your employer is rolling out AI assistants that touch customer or staff data, it's fair to ask two things: who reviews what the assistant actually did last week, and what stops it reading files it doesn't need for the task in front of it? Those aren't technical questions. They're governance questions, and "the model is smart enough to know" isn't an answer.
The sharper watch is on enforcement, not vocabulary. Vendors have a word for this problem now. What's missing is any independent evidence that the guardrails hold under pressure.
Common questions
Is Agent IBAC a standard or a product?
It's Varonis's branded approach, not an industry standard. Similar ideas are being marketed by other identity and data security vendors under different names.
Does this replace normal access controls?
No. It's meant to sit on top of existing role-based permissions and data classification, adding a check on whether an action fits the agent's current task.