Qilin ransomware group claims attack on Castle Howard Estate
The criminal group has listed the Yorkshire heritage site on its dark-web leak site. Castle Howard has not confirmed any incident, and the claim could not be independently verified.
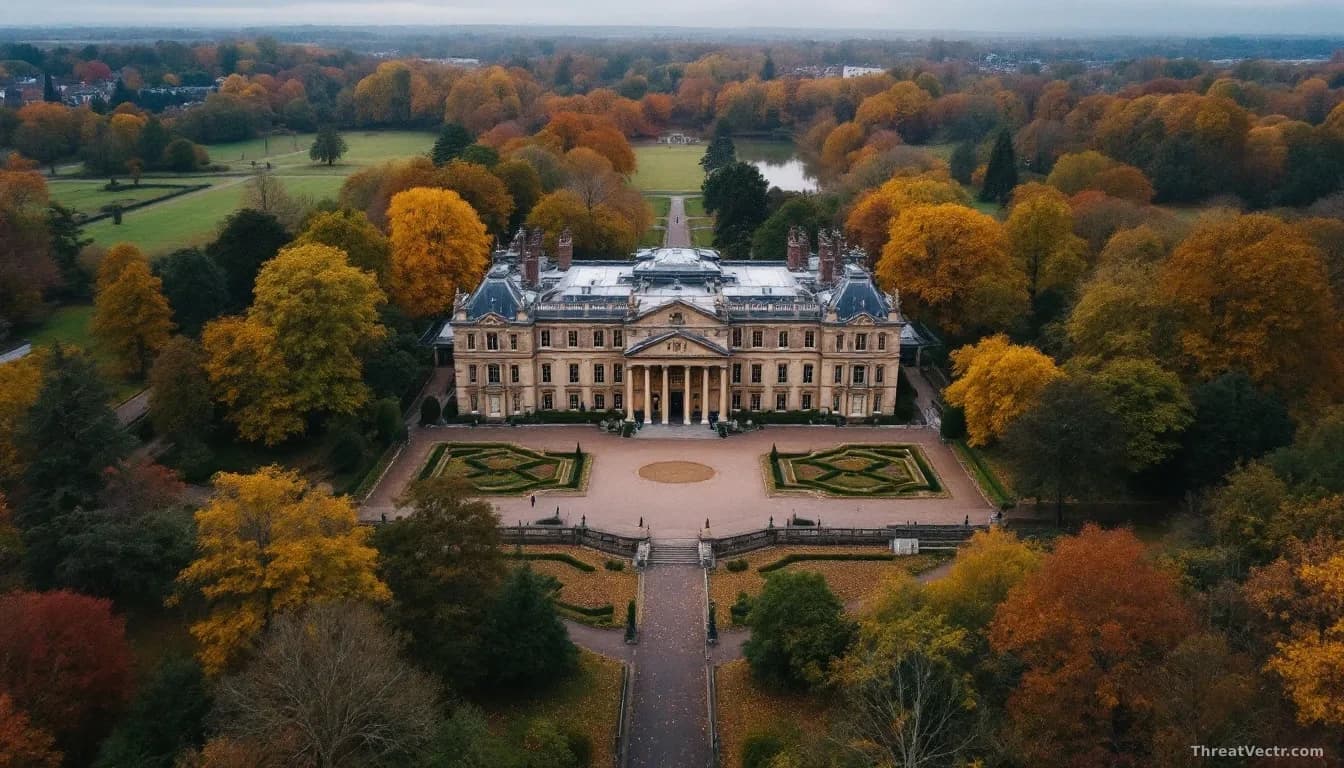
Key points
- Qilin ransomware criminals listed Castle Howard Estate, the North Yorkshire stately home and events venue, on their dark-web leak site on 24 October 2026.
- The listing contains no specific data description; the group's post reads only "N/A" where stolen file details would normally appear.
- Castle Howard has made no public statement about the claim, and it could not be independently verified at the time of publication.
- Threat Vectr has published 15 stories on Qilin, 12 of them in the past 90 days, making this one of the more consistently tracked groups in our coverage.
- Manufacturing is the sector most frequently targeted in Qilin's claimed attacks, though hospitality venues are not unusual targets.
Qilin, a ransomware group (a criminal organisation that breaks into computer systems, locks data or steals it, and demands payment to restore access), added Castle Howard Estate to its extortion list on 24 October 2026. The listing was first observed by Ransomware.live, a monitoring service that tracks such criminal announcements.
Castle Howard is best known as a stately home open to visitors and a venue for weddings and corporate events. Its systems would typically hold booking records, payment details and guest contact data, though what, if anything, was actually taken remains unconfirmed.
How seriously should this be taken?
With real caution. Ransomware leak sites are run by criminals whose goal is to embarrass companies into paying, and listings are sometimes exaggerated or entirely false. No independent evidence of a breach has surfaced.
Qilin isn't a fringe operation. We covered a Qilin claim against Pennsylvania hospitality venue Glenhardie Country Club on 11 October 2026, and the group claimed another UK-adjacent target the very next day. The pace is notable.
The absence of any stolen-data description in the post is worth watching. Most Qilin listings include at least a broad category of files claimed as proof. The "N/A" entry here could mean the group is still negotiating with the estate, that the listing is a pressure tactic issued before a deadline, or simply that the post is incomplete.
What should customers and staff do now?
If you've booked an event at Castle Howard or given the estate your contact details, a few practical steps make sense while the picture is unclear.
Watch for phishing emails, fake messages designed to look like they come from Castle Howard or a related company, that use news of this claim as a hook to get you to click a link or hand over personal details. Criminals often exploit their own leak-site announcements this way.
Be wary of any unexpected call offering "breach compensation" or asking you to confirm payment details. That's a scam pattern, not a legitimate company response.
If you reuse a password across accounts and one of those accounts is connected to Castle Howard, change it on every other service where you use the same credentials. A password manager makes that manageable.
Castle Howard's UK operations fall under the Information Commissioner's Office (ICO), the regulator that enforces data protection law in the United Kingdom. No notification from the ICO has been reported publicly, and the estate itself has made no statement.
Should you worry about Qilin specifically?
Hospitality venues hold exactly the kind of customer and payment data these groups find useful for use. The lean listing here, with no file details claimed, suggests this one may still be developing. Watch for a follow-up post from the group or a statement from Castle Howard before drawing conclusions.