Threat Intelligence — Page 21
Timor-Leste Police Arrest 314 People in Raids on Scam Call Centre Compounds
A country just 700 kilometres from Darwin has become the latest staging ground for international phone fraud, as police crack down on fortified compounds packed with laptops, SIM cards, and satellite internet equipment.
Seven booby-trapped npm packages hit Vite developers with blockchain-controlled malware
Researchers at Checkmarx say the ViteVenom campaign hides its command server across cryptocurrency networks, making it unusually hard to shut down.
Chinese Sub-Crew 'CylindricalCanine' Fingered for DigiCert Break-In
Researchers link the April 2026 intrusion at the certificate giant to an offshoot of a Chinese cybercrime group best known for chasing gambling firms.
North Korean Job-Interview Scam Hides Malware Inside Flag Images
Fake coding tests planted a four-stage stealer on developers' machines, with the payload smuggled inside SVG picture files.
Ransomware Hits Naval Contractor, Lidl Discloses Data Breach, and Iran Tracks US Military Phones
A defence shipbuilder confirms a ransomware attack, a major supermarket chain notifies customers of stolen data, and new evidence suggests Iranian operatives tracked phones belonging to US military personnel.
Why Carders Are Hunting for 'Clean' Home Internet Connections
Fraudsters are paying premium prices for residential proxies that haven't been flagged, and pairing them with fake browser identities to slip past bank fraud checks.
GoSerpent: A New Espionage Tool Quietly Targeting Southeast Asian Governments
Kaspersky says the previously unseen malware has been hitting government and diplomatic offices across the region since late 2025, with signs pointing to long-term spying rather than smash-and-grab theft.
ACR Stealer Tricks Staff Into Typing the Attack Themselves
Microsoft says a fake-fix trick is pushing a data thief onto business PCs, walking off with passwords, session cookies and cloud files.
Malware Disguised as Font Files Targets Windows Users
A global phishing campaign active since March 2026 is hiding credential-stealing malware inside fake font files, and the evasion chain is getting harder to catch.
New York Duo Charged With Laundering $43 Million From 'Pig Butchering' Investment Scams
Federal prosecutors say Zhuoying Chen and Haojie Zhang ran a shell-company money mule network that moved victim funds from Queens and Brooklyn bank accounts to China.
Russian Spies Are Testing Australia's Unlocked Doors
Australia's top signals agency has joined two dozen allied governments to warn that hackers working for Russian intelligence are quietly breaking into poorly secured network devices across critical industries worldwide.
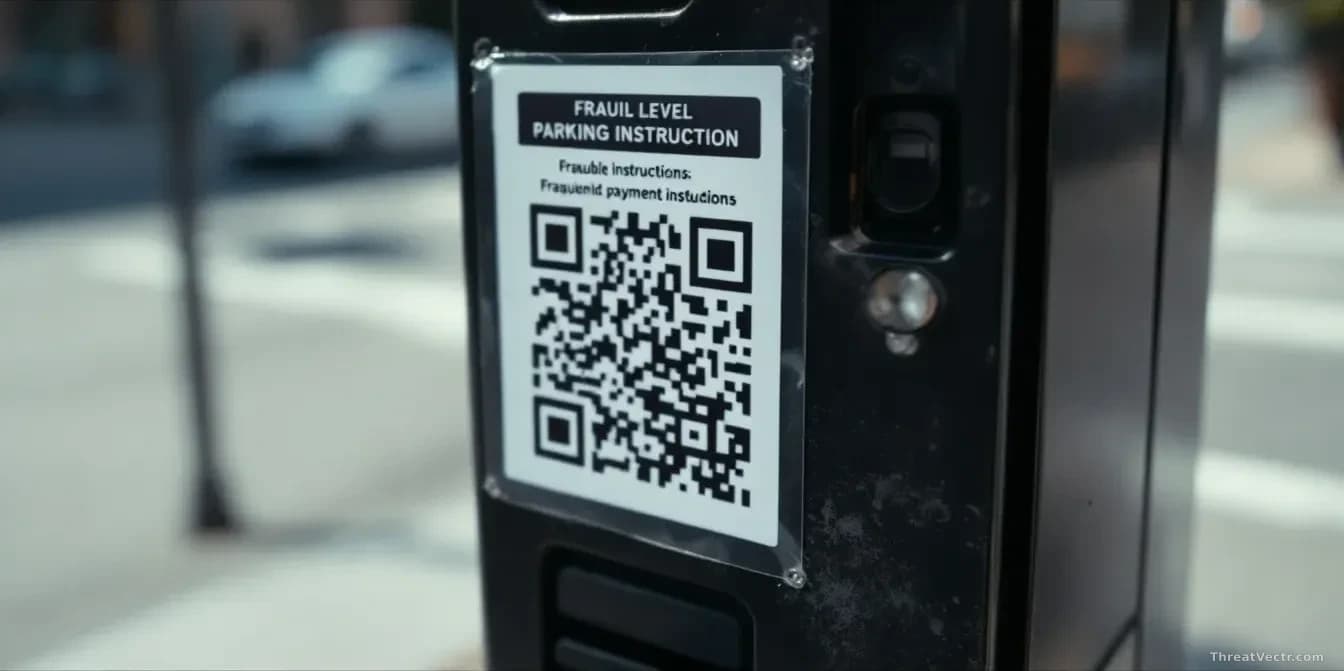
Fake QR code stickers on Christchurch parking meters are stealing payments
Scammers placed fraudulent stickers over real payment instructions to redirect drivers to copycat websites. The Christchurch City Council is urging residents not to scan any QR code found on a parking machine.
This Week's Cyber Mess: Fake Repos, Chrome Sync Stalking and a Ransomware Crew That Moves in a Day
A roundup of the week's smaller stories that share one uncomfortable theme: attacks that succeed because something looked close enough to trust.
TELEPUZ: The New Malware Hiding Behind Fake 'Fix This' Website Pop-ups
A modular info-stealer is spreading through booby-trapped websites that trick visitors into pasting malicious commands into their own computers.
Two Scattered Spider Members Jailed in UK's Largest Ever Cybercrime Prosecution
Thalha Jubair and Owen Flowers each received five and a half years in prison for a 2024 attack on Transport for London that cost the city £29 million.